You’ve seen the movie. The defense expert pats the last hair into its slicked place, adjusts his tie, and strolls confidently to the stand, with what he believes is a knowing smile on his face. Then the prosecutor asks a sharp question and the smile crumbles.
Real life is less cinematic. The digital forensics expert often never reaches the witness stand at all. Instead, his report does the talking. It lands on the prosecutor’s desk, shapes the plea discussion, and sometimes ends the case – one way or the other – before a jury is ever seated. The evidence doesn’t know who hired him, and digital “smoking guns” have a way of melting once someone looks under the hood.
When a client is facing cyberstalking or digital harassment charges, the prosecution’s case often arrives neatly packaged as a PDF of text message screenshots, a carrier call log, a few scans of filled-n forms, or a printed report from a mobile extraction tool.
To an aggressive defense attorney, that report shouldn’t look open and shut, no matter how it’s written. It should look like an invitation to start asking hard questions.
- The “Shared Device and IP” Fallacy
A text message, an IP address, or a home Wi-Fi network is not a person. A common pitfall in digital harassment cases is assuming that because a message originated from an IP address or a device tied to a defendant, that specific defendant was behind the keyboard. 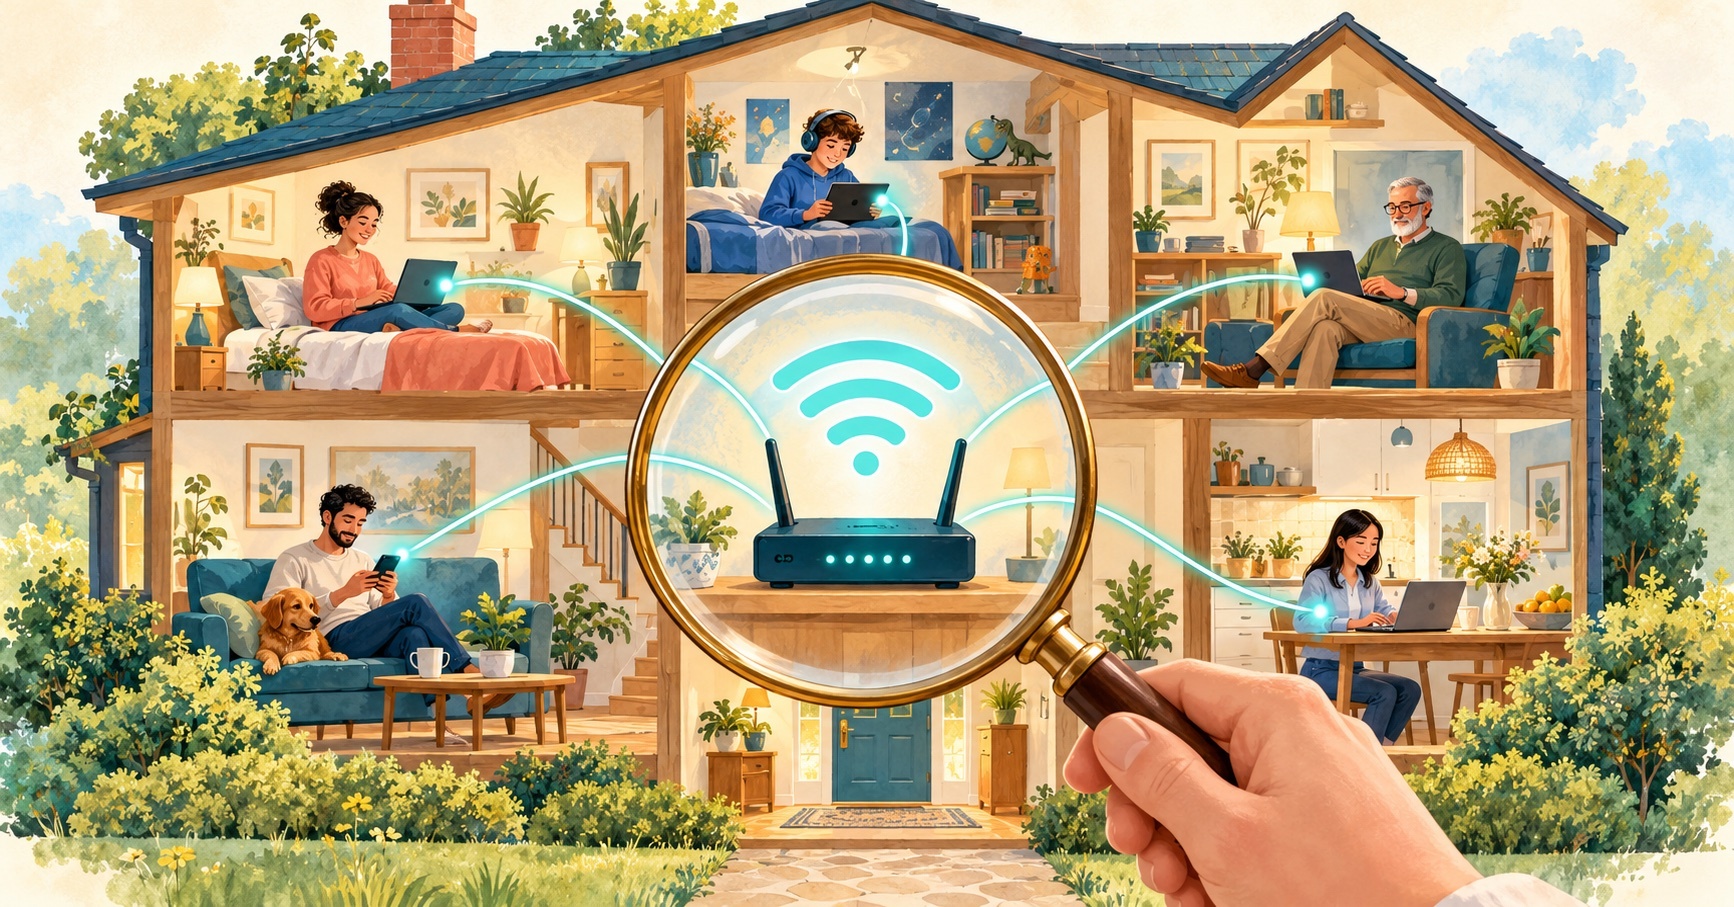
- Shared Households and Open Networks: Family members, roommates, or visiting guests or half a dozen teenagers at a gaming party in the basement, may all be on the same Wi-Fi, and to the outside world, they share a single IP address.
- Compromised Accounts & Spoofed Headers: Malware, session hijacking, or spoofed identifiers can make it look like a device sent data it never touched. Without rigorous forensic attribution, such as physical proximity logs, biometric sign-ins, or physical keystroke analysis, an IP address is just a location, not a confession.
- Context, Venting, and the Intent Gap
Prosecutors love to highlight the most inflammatory text messages out of context. But a raw chat log strips away the rhythm of a conversation.
- Was the message an isolated outburst during a bitter custody dispute, or part of an obsessive, calculated campaign?
- Is it clumsy, offensive venting, or does it meet the strict statutory threshold for a targeted, credible threat? Defense forensic work often involves reconstructing the entire communication history, including deleted messages, previous threads, and mutual exchanges. They want to show the true context of the interaction and challenge the alleged “course of conduct.”
- The Report Nobody Can Read
Extraction reports from tools like Cellebrite and Magnet AXIOM can come in a couple of flavors, and both can be a problem.
Some are enormous. Thousands of pages of call logs, app databases, Wi-Fi connections, cached images, and system entries with names only an examiner could love. The few items that matter are in there somewhere, buried under everything else the phone ever recorded. Many attorneys open one, turn a few pages, and quietly close it again. That’s understandable. Too many clients, too many pages, and a family they want to get home to sometime today. It’s also how important context gets missed.
Others are thin. A few dozen pages, cherry-picked down to the messages and records that support the charges. But a selection is not the whole phone, and what was left out may matter as much as what was kept.
Either way, ask for the full extraction in its native reviewable format, not just the PDF. Cellebrite’s Reader and AXIOM’s Portable Case let a defense examiner search, filter, and verify everything the tool captured, including what never made the printout.
- Challenging the Extraction and the Chain of Custody
Digital evidence is fragile. If law enforcement used an unvalidated tool, failed to maintain proper hashing during acquisition, or searched a seized device outside the explicit scope of a search warrant, the digital trail loses its integrity. Furthermore, third-party cloud data or ephemeral messaging apps (like WhatsApp, Signal, or Snapchat) can leave conflicting timestamps across devices due to sync delays, server backups, and local timezone mismatches.
And a timestamp doesn’t always mean what it seems to. A file’s “created” date usually records when that copy landed on the device, not when the photo was taken or the document was written. A picture shot in 2019 and texted to someone last week may show a creation date of last week on the recipient’s phone. It’s less like a postmark and more like the “received” stamp on a letter. Which date the report shows, and what that date actually measures, can change the whole timeline.
What This Means for Defense Counsel
If you are defending a cyberstalking or digital harassment case, never take a prosecutor’s printout of digital communications at face value. I wouldn’t jump straight to assuming something was hidden on purpose, either. Often it simply wasn’t asked for. Cut them a break: prosecutors carry heavy caseloads too, and nobody thinks of everything. There may be something they didn’t think to ask for that you can. And a clean PDF export can’t show you the metadata, the sync artifacts, or the gaps in the timeline.
The data is the data, and it often tells a very different story once you examine the underlying extraction files.
Have you ever had a digital evidence trail completely unravel under forensic review? I’d like to hear about your courtroom experiences with electronic evidence.
Questions about digital attribution, device artifacts, or analyzing electronic communication patterns? Burgess Forensics examines system logs, mobile artifacts, metadata, and other digital evidence. (866) 345-3345 | steve@burgessforensics.com